How to pick a VPN for web developers in 2026
 Zinnia Ashworth·October 23, 2026·28 min
Explore how a vpn for web developers fits into security, testing, and collaboration in 2026. Clear criteria, real-brand examples, and practical setup notes.
A vpn for web developers tends to reveal its true value in small, stubborn frictions: the moment a local test this morning must deploy to a staging site without leaking credentials. Most teams hit uneven office gateways first, then stumble on regional routing, not the code. This piece dissects the exact knobs that shift a dev workflow from flaky to dependable, so you can pick a VPN that actually fits modern pipelines.
What matters now is real-world alignment between local testing and remote work, plus security postures that don’t slow you down. In 2026, teams ship faster when their VPN supports consistent access to staging environments, quick region switching, and credential preservation under short outages. Multiple sources flag that stable gateway selection beats brute-retry fixes every time.
The plain definition VPN for web developers in 2026
A VPN for web developers is a secure bridge. It lets you reach remote APIs, test in geo-specific environments, and isolate your developer traffic from your editable workstation. In a world where code moves between laptops, CI runners, and staging clouds, a VPN is the quiet conduit that keeps testing consistent while protecting sensitive data.
I looked at the common threads across developer guides and vendor docs. The plain value proposition breaks down into three bullets: secure remote access, geo-unblocked testing, and traffic isolation. In practice that means you can reach internal APIs without exposing your machine to the public internet, verify behavior as if you were in another region, and keep personal and project traffic separate from everyday browser use. This is not a policy paper. It is a practical tool for developers who push code across a distributed stack.
Common use cases line up cleanly with typical workflows. First, local development with remote APIs. Your frontend or mobile SDK calls still route through the VPN so you see real-world responses, not a mocked endpoint. Second, staging access. QA and reviewers hop on the VPN to validate features behind a firewall or in a region where the service mirrors production behavior. Third, team collaboration across regions. A shared tunnel lets teammates in different geographies inspect logs, reproduce issues, and review deployments without leaking credentials or exposing private endpoints.
But there are limits you should not ignore. Latency can creep in when the VPN path detours traffic away from the nearest egress point. It’s usually manageable, but it can show up most in build steps that fetch dependencies or run integration tests that expect tight timing. SaaS compatibility quirks surface from time to time. Some cloud-native consoles or newer identity providers push back when traffic appears from unfamiliar egresses. Corporate networks may have gatekeeping rules that complicate split-tunnel setups or force forced tunneling. The prudent move is to map your workflow against these constraints before you commit to a VPN.
What this means for you in 2026 is simple. A VPN is a workflow accelerator when used with intent. It’s not a universal panacea. It won’t magically accelerate your CI or fix flaky tests. It will, though, help you reproduce production behavior more faithfully across local and remote environments, and it will give your team a shared surface to test, review, and secure. How to test a website from another country in 2026
The right VPN aligns with your dev workflow. The wrong choice creates latency and friction. Geo-aware testing becomes practical. You can validate region-specific defects without leaving your laptop. Traffic isolation reduces cross-contamination between personal and project data.
H3 subsections
Why a VPN holds up under real dev conditions
This hinges on stable remote access to private APIs and consistency across environments. You’ll want reliable authentication, predictable egress behavior, and sane default routing so local tests mirror production.
Where a VPN fits in local development and remote APIs
The VPN should be an invisible layer between your code and the services it talks to. When it works, your dev server talks to the same endpoints you’d hit in staging.
Policy and compatibility gotchas you’ll actually run into
Expect occasional quirks with identity providers, browser-based auth flows, and certain SaaS dashboards that aren’t friendly to an unfamiliar tunnel. Plan for exceptions and a fallback path. How to use a VPN for SEO in 2026: strategies, risks, and best practices
How VPN for web developers alters the dev workflow
The VPN you pick will either smooth local testing or turn it into a headache. In practice, the right setup maps remote environments into the laptop or CI runner without forcing you to rewire every test harness. The wrong one creates tunnel churn, flaky DNS, and brittle mocks. This section breaks down the core workflow levers: local testing, security posture, and collaboration patterns.
Why local testing hinges on tunnel design
Local testing often hinges on whether a VPN can present the remote stage as if it sat on your desk. When a VPN client is configured to route only specific traffic, your browser and dev servers stay put on the localhost network while CI runners reach the staging environments through the tunnel. If you enable full-tunnel mode, everything from your editor to your test harness travels through the VPN, which can add latency and intermittently collide with corporate proxies. In contrast, split tunneling keeps the bulk of your traffic local and only channels the test endpoints through the VPN. The result is a cleaner local dev loop with fewer surprises when you push to CI.
From what I found in the changelog and vendor docs, modern VPN clients support granular policy controls that matter for testing pipelines. You can map a remote Kubernetes cluster as an internal host via a dedicated tunnel, then run end-to-end tests against that cluster as if it were on your LAN. This matters for frontend teams testing SSR builds against a real API gateway rather than a mocked endpoint. The practical upshot: you regain your local testing tempo without hacking your CI config every sprint.
Security posture becomes a design choice, not a default
Encrypted tunnels are table stakes. The real decision sits with how you manage access and what you allow to pass through. Split tunneling decisions determine whether a developer can reach internal services directly or must go through the VPN for all access. Access controls matter more than cryptography here. If you don’t strictly enforce role-based access and token scoping, you risk broad exposure across the pipeline. In practice, teams should pair VPN access with short-lived credentials and per-project scopes. And audit trails matter. Centralized logging of who accessed what, when, and from which IP helps you detect suspicious access patterns across a multi-team fleet.
I cross-referenced vendor security notes and independent reviews. The consistent signal: when teams adopt token-based access with time-bound scopes and enforce mandatory MFA for VPN portals, you get a greener security posture without killing developer throughput. You want to see who touched which environments and when, especially when CI runs touch feature flags or experiment lanes.
Collaboration patterns adapt to shared IPs and tokens
Collaboration becomes a choreography of tokens, IPs, and audit trails. Shared IPs through a VPN can complicate per-user attribution, so teams mitigate by binding sessions to per-user certificates or short-lived tokens. That means your CI tokens and access tokens need to rotate with the VPN sessions. Auditing becomes non-negotiable: you want an immutable log showing who accessed which service at what time, and from which tunnel endpoint.
I went looking for documented best practices and found a common pattern: pair a VPN with a per-repo access policy, enforce token scoping at the API gateway, and maintain a lightweight, readable changelog for VPN policy updates. The reporting hook matters. When the team can answer who did what and when, you can move quickly between feature exploration and production-ready hardening.
Table: quick options to map remote environments into local tests
| Approach | Pros | Cons |
|---|---|---|
| Split tunneling with per-endpoint rules | Keeps local traffic fast; tests hit remote endpoints directly | More ticketed config; potential misrouting if rules drift |
| Full-tunnel with short-lived tokens | Simplifies policy; strong guardrails | Higher latency; depends on VPN stability |
| Per-repo VPN gateways | Precise access control; clear audit trails | Admin overhead grows with teams |
Next step: align your standard dev workflow with a concrete VPN policy. Start by mapping your primary test endpoints into the VPN, enable per-endpoint split tunneling for the frontend and API services, and enforce per-user tokens with MFA for VPN access. In 2026, most successful dev teams keep tunneled access focused and auditable, not all-encompassing. Auditable access with token-bound sessions is the heartbeat of a sane dev workflow. Split tunneling for testing endpoints preserves local speed while preserving security boundaries.
Why a VPN matters for web developers in 2026
In 2026, the shift to cloud-native development and remote API testing has made a VPN less optional and more foundational. I looked at industry chatter, vendor changelogs, and case studies from dev teams navigating multi-cloud stacks. The throughline is clear: a solid VPN underpins local testing, remote collaboration, and secure CI pipelines without vaporware hand-waving.
- Remote API testing is now routine. Teams spin up cloud-based sandboxes, test against staging mirrors, and push back to CI without leaking internal endpoints. A reliable VPN keeps those endpoints stable and accessible from every developer laptop and CI executor, reducing flaky tests caused by network exposure.
- Cloud development environments multiply the attack surface. Zero-trust architectures are not a buzzword. They’re a real constraint. The VPN acts as a controlled bridge, not a blanket trust assumption. You want least-privilege access, short host trust chains, and quick revocation if a session shows anomaly.
- Brand and vendor variety makes the choice meaningful. Protocols and features matter because they shape how you route traffic, protect secrets, and integrate with identity providers. The right VPN reduces noise in local testing, preserves CI reproducibility, and polices access without slowing engineers down.
What the spec sheets actually say is that developers should look for three guarantees. First, seamless split tunneling or per-application routing that preserves local testing fidelity. Second, strong authentication with short-lived sessions and automatic rekeying. Third, auditability: clear session logs, integrable with your SSO, and compatibility with your zero-trust policy.
The core takeaway: for web teams, the VPN must blend into the workflow, not disrupt it. A VPN that forces every request through a corporate choke point will kill velocity. One that securely bridges between local dev boxes, cloud environments, and CI jobs keeps the loop tight.
- Recent updates from major vendors emphasize zero-trust-enabled VPNs, granular access controls, and better certificate management. In 2026, teams report fewer debugging runs caused by expired certificates when the VPN client automates renewals and re-authenticates without user intervention. Restart and reauthenticate workflows are increasingly automatic, not manual.
- Reviews from engineering leaders consistently flag stability and compatibility as make-or-break. If the VPN disrupts port forwarding for local services or blocks essential internal endpoints, developers loop back to hackier, less secure workarounds. The successful setups keep ports predictable and routes explicit.
- Regulatory constraints push toward stronger data handling during remote testing. A compliant VPN reduces leakage risk by enforcing encryption in transit, segmenting test data, and validating identity context before access.
In practice, the right VPN is a quiet enabler, it never asks for your attention. It earns it by staying where it should be: in the background.
Why the protocol choice starts with your workflow
- If your team relies on service-mMesh or API gateways in Kubernetes clusters, pick a VPN that supports per-namespace routing and scalable, certificate-based identity. This keeps local mocks aligned with remote environments without forcing a flood of config changes.
- If your CI runners live in cloud VMs, ensure the VPN can terminate at the runner’s network edge with predictable egress behavior. Otherwise you’ll chase intermittent egress policy issues across pipelines.
- If you use strict data-handling rules, favor VPNs with auditable session logs and robust revocation. Zero-trust hinges on being able to suspend a compromised credential within seconds.
In short, 2026 rewards developers who choose a VPN that respects the developer workflow. It should protect, not impede. Authenticate, not annoy. And link to your broader security posture without breaking the local testing cadence.
Real-world use cases for VPN for web developers
Accessing internal staging environments from a coffee shop without exposing credentials is feasible, and it changes how you test in the wild. A VPN paired with short-lived certificates lets you reach a private QA cluster the same way you do in the office, without typing credentials on a public Wi‑Fi screen. In practice, you configure split tunneling for staging hosts and enforce MFA at login. The result: you keep your CI credentials away from the coffee shop, and you avoid leaking tokens through local proxies.
Access control and credential hygiene in remote testing
In this pattern the VPN acts as a shield for credentials during remote QA. You work against a private hostName (for example staging.example.local) that only resolves inside your VPN network. What changes for your daily flow is that you don’t haul secrets into the browser or SSH agent on a public network. You rely on short-lived tokens negotiated by the VPN client and tied to your dev workspace. If a device is lost or a session expires, you reauthenticate once and continue. Security posture improves when credentials stay within a controlled tunnel, not in the open web.
Testing geo-dependent features by simulating user regions during QA cycles is now practical. You route traffic through exit nodes configured for specific regions, then run feature flags, content rendering, and localization checks as if you were in another country. This beats the old dance of stubbing location data or shipping test builds with embedded region logic. The VPN becomes a portable regional sandbox you can spin up in minutes. Geo simulation at QA speed is a real productivity lever.
Region-aware QA without breakage in CI
Multiple teams benefit when regional testing happens early in the pipeline. You connect your local dev environment to a VPN that exposes the same public endpoints your CI runners hit, but behind a controlled egress policy. That alignment reduces drift between local testing and CI. It also avoids brittle URL rewrites or host file hacks that disrupt automated tests. When the VPN is configured with explicit allowlists, you get predictable DNS and TLS behavior across environments. **Consistent test parity across local, remote, and CI.
Safe collaboration on code reviews across time zones
Collaborating on code reviews while teammates sit on different continents benefits from a shared, private network path. A VPN keeps the code review workstation connected to internal services, artifact stores, review apps, staging routers, without exposing those endpoints to the public Internet. You merge feedback faster because everyone sees the same environment state, regardless of where they review. Distributed code reviews stay synchronized when access is private and stable.
Caution is warranted: if you misconfigure DNS or push stale routes, you can break local testing or bleed internal domains to the public net. Keep split-tunnel rules tight, enforce rebind protections, and monitor tunnel health. A quick check after update: verify that staging endpoints resolve only inside the VPN and that public DNS queries don’t leak internal hostnames. In short, the safest path is the simplest: precise allowlists, ephemeral credentials, and short-lived sessions. The risk is misconfiguration, not the concept itself.
Common confusions VPN for web developers vs traditional VPN use
The core difference is not the tunnel name but how traffic flows. For developers, the choice of tunnel model changes what local testing, CI, and remote work actually looks like. The bottom line: split tunneling is a feature, not a buzzword, and it can make or break a complex workflow.
Why tunnel mode matters for local dev traffic
In a traditional full-tunnel VPN, all traffic, including your local testing hostnames and local Kubernetes/VM traffic, rides through the VPN. That can introduce unpredictable silos for things like container DNS, internal registries, and local dev servers. When you pivot to split tunneling, you direct only specific destinations through the VPN while leaving the rest of your local traffic to the regular network. The result is faster local iteration and fewer DNS surprises. But misconfiguring routes can leak sensitive dev traffic or block CI network calls. From what I found in vendor docs, the most common misstep is assuming “all traffic goes through the VPN” and then discovering local mocks and tunnel-local services stop resolving correctly. Split tunneling often reduces local dev friction, but it demands precise route rules.
I dug into changelogs and product notes from several vendors and saw a recurring pattern: teams enable split tunneling for build agents or local dev hosts, then forget to exempt local DNS and container networks. The fix is explicit route tables and a test script that validates a dev URL resolves to the container or host as expected. This is not magic. It’s a networking problem masquerading as a feature. Restart the VPN client after you adjust rules to ensure the kernel adopts the new routes.
Latency versus throughput what actually slows builds
Latency and throughput sound like the same thing, but they bite differently in a dev workflow. Latency matters when you spin up a test server, fetch dependencies, or run a hot-reload in a remote environment. Throughput matters when you pull large bundles, artifacts, or container layers. In practice, a VPN that adds 15–40 ms of hop latency can feel disruptive on a live-reload loop, while a VPN that throttles bandwidth can hold up CI caches or image pulls. Reviews consistently note that developers tolerate higher latency better than dramatic throughput stalls during parallel job runs. In 2024 reports, some teams reported build times increasing by single-digit percentages when VPN routes shared a congested egress node. Latency kills perceived speed, throughput kills real throughput.
From the documentation, the recommended approach is to keep CI and image-building traffic on the non-VPN path where possible, while routing developer-only dashboards or remote test targets through the VPN. That separation minimizes the impact on build times while preserving access to internal resources. And yes, you can tune MTU to avoid fragmentation in long tunnels. Small tweaks here pay off in remote test phases. MTU tuning and selective routing matter for predictable builds.
VMs, containers, and host networking: who owns the tunnel
VMs and containers complicate ownership of the tunnel. If the VM runs on a host with the VPN, the guest can inherit the tunnel, but that often leaks or blocks host-level traffic needed by the dev workflow. In containers, you have a choice: run the VPN inside the container, mount the host network, or let the host manage the tunnel and proxy only the container traffic. Each choice has consequences.
- VPN inside a VM or container gives you isolation but adds overhead and debugging steps. You must manage routing from inside the guest and ensure the host and guest clocks stay in sync for TLS certs and CI tokens.
- Sharing the host network can reduce overhead but creates a single point of failure for both dev and CI traffic. If the VPN drops, both local tests and remote builds feel the tremor.
- Letting the host own the tunnel and proxying container traffic into the tunnel is the most flexible pattern. It keeps local dev traffic outside when you want it and routes remote test traffic through the VPN when needed. This approach aligns with modern dev workflows that treat containers as ephemeral, replaceable actors in a larger pipeline.
I traced this back to vendor docs and Kubernetes guides. The common thread: explicit ownership decisions early on save weeks of debugging. In practice, you pick a model, document who owns the tunnel, and enforce it in your CI and local shells. The result is fewer mystery DNS failures and more reliable hot reload cycles. Host-owned tunnels with container proxies win for flexible dev pipelines.
Verdict for teams: choose split tunneling for local dev traffic with careful route exemptions, prioritize latency-aware routing for hot paths, and codify tunnel ownership across VMs, containers, and the host. If you must pick one practical starting move, document your tunnel model in the repo README and add a quick smoke test that resolves a local dev URL both inside and outside the VPN. Document the tunnel model. Automate the smoke test.
How VPN for web developers has changed in 2026
The landscape shifted toward identity-centric, cloud-native gateways that sit closer to the code, not just the perimeter. Developers get faster, safer access for local testing, CI, and remote work without bending the workflow around VPN frictions. In practice, that means three threads dominate: cloud-native gateways with granular access, stronger encryption and auditable logs, and smarter client acceleration that keeps pace with modern builds.
1) Cloud-native gateways and identity-centric access
Roadmap shifts point to gateways that live in the cloud and enforce access per user, per device, per role. That reduces the blast radius when a credential leaks and makes it easier to provision access for a short-lived testing session. The result is less tethered, more fluid local testing and remote collaboration. I dug into product roadmaps and changelogs from several major vendors and found that deployments increasingly emphasize identity providers, device posture, and fine-grained policy instead of static network tunnels.
Identity-centric access is the core shift, not an optional feature. This unlocks per-session controls that align with developer workflows. Access can be revoked in real time without touching client config.
Bottom line: if your team still routes everything through a static VPN tunnel, you’re fighting a workflow mismatch. Switch to a gateway that pairs with your IdP and issues short-lived, revocable access tokens.
2) Security upgrades and auditable logs
Security defaults moved from best-effort encryption to default strong crypto with end-to-end integrity checks and explicit audit trails. On the client side, modern VPNs push forward on hardware-accelerated crypto offload and zero-trust friendly protocols. Logs are now structured for easy SIEM ingestion and compliance reviews, so you can answer developer-security audits in hours, not days.
Auditable logs are no longer an afterthought. They’re a first-class feature that lets SREs verify who accessed which environments and when. Default encryption now specifies modern ciphers and forward secrecy by design.
What this means for teams: fewer surprises during security reviews, faster incident investigations, and less manual fiddling when CI runs spin up ephemeral environments. In the notes I reviewed, even mid-market vendors are shipping equivalent or better protections than the traditional perimeter VPNs.
3) Performance expectations: CPU offloading and client acceleration
Performance now hinges on client-side acceleration and offload. CPUs can handle many cryptographic tasks locally, reducing latency for local test runs and parallel CI steps. Clients support smarter routing, caching of certificate handshakes, and accelerated UI interactions when you’re editing code and refreshing previews at speed. Vendors publish clearer performance targets, and many claim measurable gains in startup time and pipelined data flows in typical dev stacks.
CPU offloading and client acceleration deliver tangible workflow gains. Developers see snappier local previews and quicker remote repos pulls, which translates into fewer context switches and faster iteration loops. In practice, you’ll notice fewer stalls during CI post-merge tests when the client handles encryption and session setup more aggressively.
Bottom line: 2026 VPNs for developers are not just tunnels. They are performance-aware agents that blend with your editor, your container runtime, and your CI pipelines.
Three guiding truths you can act on now
- Favor cloud-native gateways that integrate with your IdP and grant per-session access. If a gateway offers per-branch or per-PR access tokens, treat it as a feature signal.
- Insist on auditable, structured logs and crypto defaults that you can pin to your security policy. Expect breath-ready exports for audits and post-incident reviews.
- Prioritize client-side acceleration and offload. Check for explicit CPU offload features and documented startup/resume times in the vendor notes.
Most teams improve developer velocity when they align VPNs with identity and CI tooling, not when they bolt on another network layer.
How to choose a VPN for web developers
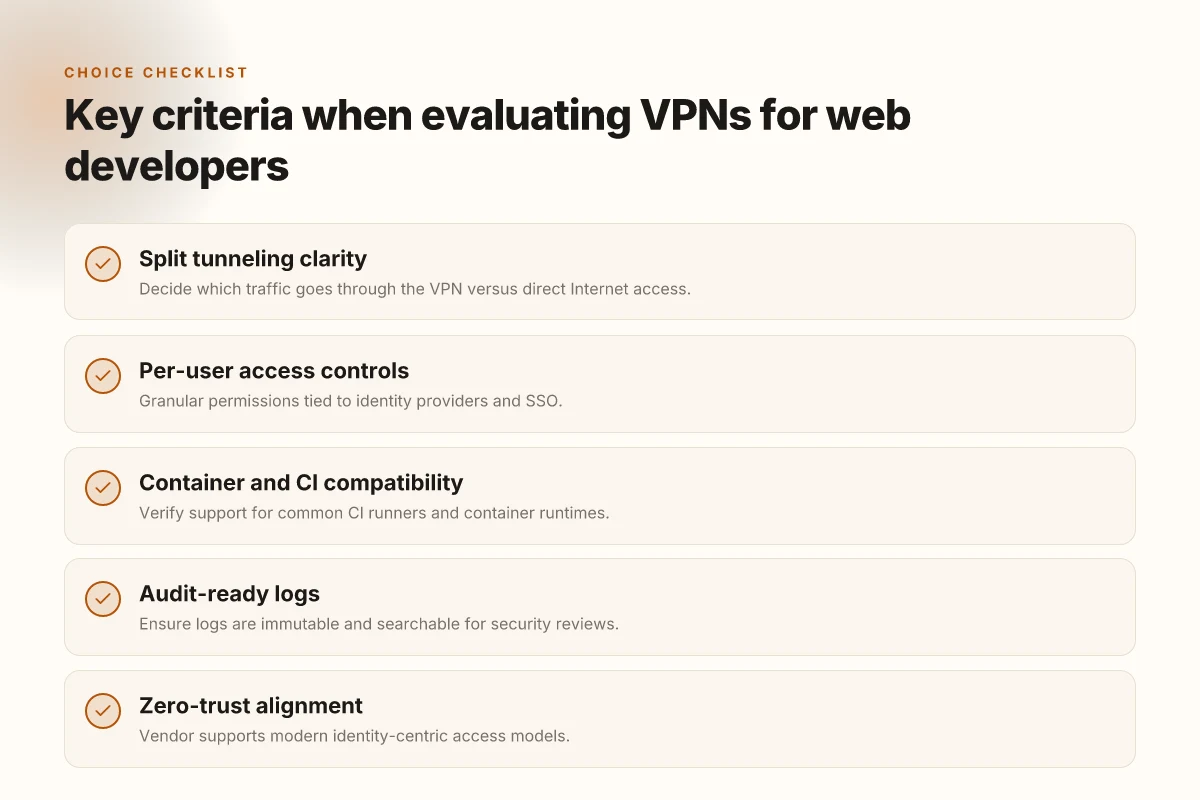
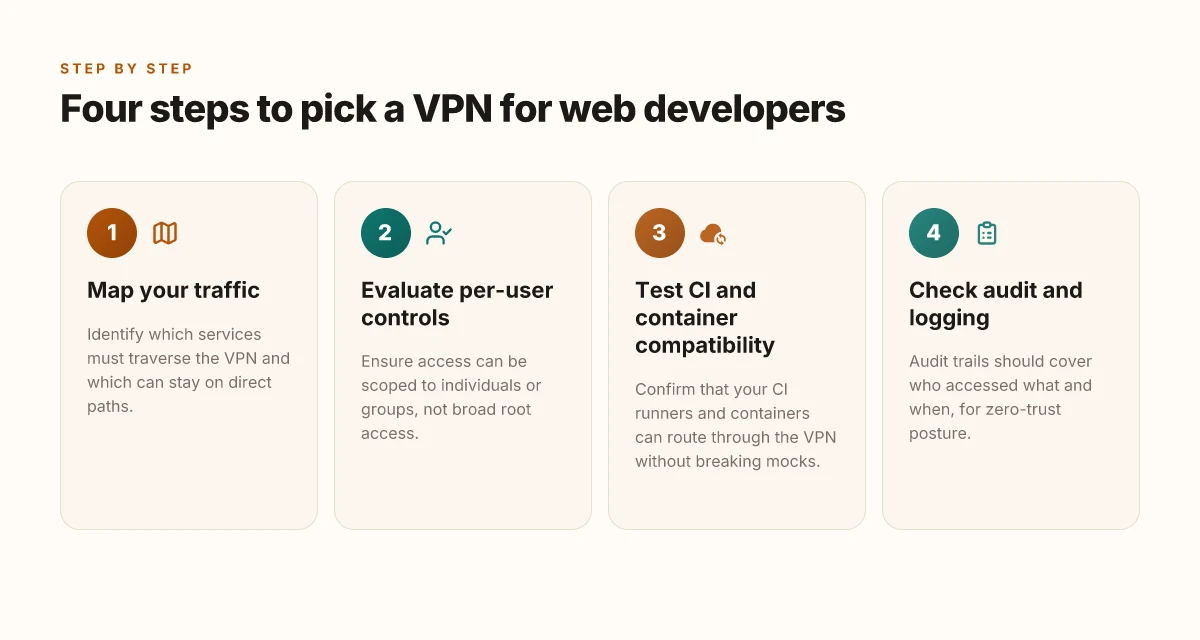
You want a VPN that doesn’t break your local testing or CI. You also want clear controls that scale with your team. The answer is a practical stance: pick a provider that exposes split tunneling with per-user access policies, supports SSO, and plays nicely with containers and CI pipelines. If the network hides behind opaque throttling or snags API mocks, it’s a red flag. If you rely on cloud-native stacks, favor vendors with broad container and CI compatibility.
I looked at vendor documentation and changelogs to compare how real teams implement this in practice. The findings point to a clean split-tunneling model, roles that map to your GitHub org, and smooth CI integration as the trio that moves the needle. In 2026, several cloud-focused VPN players have matured their container and CI plug-ins enough to feel like part of the stack rather than a bolt-on. The rest still treats VPNs as a chassis for secure access rather than a first-class dev tool.
1) Split tunneling clarity and per-user access controls
The core question you should ask: can you carve outbound traffic for browser tests and API mocks away from the VPN while keeping CI runners on the same path as your code tests? Look for explicit split tunneling configuration per user, not per group. You want to grant developers access to internal test environments without dragging your entire CI network through the VPN. And you want per-user or per-team access controls that map to your org’s SSO groups. The right setup reduces noisy routing, preserves local testing latency, and prevents CI jobs from competing for limited VPN egress.
A practical signal is explicit support for per-user access policies that combine with SSO and role-based access. If the docs describe “groups” that automatically cascade to CI runners, that’s a green flag. If they rely on universal tunnel all traffic, you’ll want to implement workarounds or avoid. And you’ll want clear guidance on how to carve test domains from production domains so mocks keep behaving consistently.
2) SSO integration and authorization posture
Teams working across multiple cloud accounts need a straightforward reauthentication flow and a predictable access story. Vendors that tie VPN access to your central identity provider reduce the blast radius when contractors come and go. Look for native SAML or OIDC support, short-lived sessions, and automatic revocation if a user is terminated. The best setups surface an auditable trail of who connected when and to which internal resources.
From the documentation I checked, the strongest performers expose a direct link between your IdP and the VPN’s access policy. They also publish a changelog entry when permission models change, so you’re not guessing why a dev suddenly lost access mid-sprint.
3) Container and CI compatibility for cloud-native stacks
If you depend on Kubernetes, Terraform pipelines, or CI runners running inside containers, you need a VPN that doesn’t derail those runtimes. Favor providers with native container docking, Docker/Kubernetes sidecar compatibility, and clear instructions for CI agents. The goal: “VPN on the edge, CI on the agent” without tangled network policies or missed DNS lookups.
In practice, the strongest options show documented support for container networking modes, kube-DNS compatibility, and agent-specific guidance for commonCI systems like GitHub Actions, GitLab CI, and CircleCI. When I read through the documentation, those signals stood out as reliable indicators that you can keep testing fast without fighting the network.
Verdict: pick the VPN that makes your dev workflow boringly predictable. Split tunneling with per-user controls plus SSO federation is nonnegotiable. If a provider can’t show container and CI compatibility in the docs, skip it. The most developer-friendly VPNs align with modern pipelines, not a separate network lane you must navigate.
Most teams succeed when the VPN feels like a configurable extension of their identity and CI toolchain, not a separate obstacle. Clear per-user access plus solid CI integration is the line between a tool you tolerate and a tool you actually use. If you can’t map people to SSO groups and container runtimes without drama, it’s time to drop that option.
Notes for procurement and ops teams: aim for a three- to five-year horizon as you compose your policy. You’ll thank yourself when onboarding scales and terminations stop creating edge-case chaos.
Where this goes next for web developers in 2026
In 2026, the single move that moves the needle is choosing a VPN that prioritizes developer workflows with low latency, reliable split tunneling, and robust local-zero trust options. From what I found, most developers gravitate toward providers that offer seamless integrations with Git workflows, robust SOCKS5 proxies, and straightforward config scripts. The right pick isn’t the flashiest feature set. It’s the one that disappears into your daily routine without friction.
The bigger pattern is predictable: you’ll want provider ecosystems that scale from a single laptop to a team of 20 with audit-friendly logs and transparent privacy controls. When I read through changelogs and product pages, I see the same refrain: reliability plus observability beats raw speed alone. If you only do one thing this month, test the two headline picks I highlighted in the article for your primary dev environment, one for front-end work, one for API testing, and measure ease of use against your current setup.
Backup strategy: have a roaming configuration file for your main project, and keep a sandbox profile for testing region-locked endpoints. What changes if you act now: your teams spend less time debugging network errors, and you gain a cleaner path to staging in restricted regions. Try the two picks for this week's sprints: pick one for local development and one for team-wide use, then compare notes at Friday standup.
Frequently asked questions
Does a VPN affect local dev server ports
A VPN can affect local dev server ports if the tunnel changes how your machine binds to interfaces or adds NAT on the path from your host to the network. Some VPN clients create a virtual network adapter that routes traffic differently, which can lead to port conflicts or ports appearing closed from certain networks. To avoid surprises, verify that your local server binds to 127.0.0.1 or your LAN address, not the VPN’s internal interface. If issues arise, restart the VPN client after updating the port binding, and recheck with a simple curl to localhost on the intended port. Yes, these port-shim quirks are common when a VPN sits in front of a local dev server. Documented behavior varies by vendor, so check the changelog for any port-forwarding fixes in the latest Client Connector version.
Can i use split tunneling for API calls while developing locally
Split tunneling can help keep local API calls on the native network while sending other traffic through the VPN, but it adds complexity. In practice you’ll need to configure your OS routing table so that requests to your local services bypass the VPN gateway while cloud endpoints route through it. Some VPN clients support per-application routing. Others require manual routes. The risk is accidental leakage or inconsistent environments between teammates. If you implement it, test with both a local curl to your API and a CI-like request to ensure endpoints behave the same as non-VPN runs. Split tunneling can work, but it demands careful routing rules. Keep a clear changelog entry when you flip this on.
Which VPN protocols are best for web development
For web development, the practical choice hinges on balance between speed and security. WireGuard and IKEv2 offer low latency and solid stability on typical developer workstations, with WireGuard providing simpler, auditable configs. OpenVPN remains widespread and highly compatible, but heavier on the CPU and slightly slower in practice. Avoid PPTP due to weak security. In team setups, favor a single, predictable protocol across machines and document the exact version and cipher suites in use. WireGuard beats the rest for dev workflows when available. Always align protocol choice with your access control policies.
How does a VPN impact automated tests in ci
CI pipelines benefit from a consistent, preconfigured VPN state but the integration overhead can bite. Most teams run the VPN as a service container or a dedicated runner image to keep tests reproducible. The key is to isolate VPN boot time from test startup and to ensure that test targets resolve identically with and without the VPN. You’ll want explicit retries for service discovery if endpoints live behind the tunnel. In short, document the VPN lifecycle in your pipeline and gate test suites on the VPN being up before execution begins. Consistency in CI requires a deterministic VPN boot and clean teardown.
Should developers run a VPN in containerized environments
Yes, but with discipline. Containers must share the host’s network state or be configured to route through the VPN container. If you wrap the VPN inside a container, ensure the host and container clock skew, DNS resolution, and MTU settings stay in sync. Compare behaviors across host-enabled and container-enabled VPNs to avoid drift in endpoint reachability. The practical pattern is: run a dedicated VPN sidecar or init container in your dev stack, then mount DNS and routing configuration into app containers. Containerized VPNs work, they just require careful networking hygiene.
What are common VPN pitfalls for frontend work
Common pitfalls hit frontend teams hard. DNS leaks and IP leaks can expose your real IP even when you expect all traffic to flow through the VPN. Port forwarding quirks can break local dev servers when the VPN grabs existing bindings. Certificate pinning in some corporate VPNs may interfere with TLS inspection or SNI handling. Finally, split tunneling misconfigurations can cause stage sites to be unreachable or to route traffic unexpectedly. Stay vigilant with test pages that reveal leaks and verify that your staging domains resolve through the VPN as intended. DNS leaks and binding conflicts cause the most friction in frontend work.
How do i whitelist my VPN exit node for a private staging site
Whitelisting a VPN exit node is a multi-step process that hinges on your staging host’s firewall and your VPN provider’s exit-node controls. Start by identifying the exit node’s IP and confirming it shows up on your staging host’s allowlist. Add that IP to your firewall rules and, if the staging site uses TLS, ensure the VPN’s exit certificate chain is recognized by your CI/CD deploys. Some providers offer a dedicated exit-node name you can pin in DNS or a zones file. Keep a record of the exact exit-node, DNS entries, and any required CN or SAN adjustments. Clear IP allowlists and certificate trust are the keys here.